GeoServer 夏季安全更新汇总:零日漏洞、供应链风险与 AI 辅助报告新政策
GeoServer 项目近日发布了 2026 年夏季安全公告回顾,汇总了近期公开的多个通用漏洞与暴露(CVE),以及一起影响该项目的供应链安全事件。这一系列活动也促使项目方更新了安全政策,新增了针对 AI 辅助漏洞报告的指导内容。 对于负责 GeoServer 实例的管理员而言,核心建议非常明确:请尽快升级至 GeoServer 3.0.1、GeoServer 2.28.5 或 GeoServer 2.27.6 版本。GeoServer 项目遵循协调漏洞披露政策,即在 CVE 详情公开之前,先为稳定版和维护版发布修复程序,以便所有用户能在公开披露前完成更新。 2026 年 8 月,GeoServer 遭遇了一次零日漏洞事件——即在没有已知修复方案的情况下,漏洞已被在野利用。该问题此前已由多位独立研究人员私下报告,修复程序也已安排在 GeoServer 3.0.1 版本中发布。然而,一个与项目及报告研究人员均无关联的第三方在社交媒体上公开披露了该漏洞,导致情况迅速恶化。公开帖子发布后数小时内,便检测到了针对该漏洞的扫描行为。此次事件响应速度极快,引发了新闻报道,并在用户论坛上发布了紧急更新呼吁。项目方特别感谢记者 Ravie Lakshmanan 通过开源地理空间基金会(OSGeo)第一时间通知了项目领导层。 此次发布的 GeoServer 3.0.1、2.28.5 和 2.27.6 版本主要修复了以下关键漏洞:CVE-2026-76904——jsonArrayContains 过滤函数中的未认证 PostGIS SQL 注入(严重级别)。该漏洞存在于 GeoTools 中,利用条件为需要 Text 或 JSON 列,影响 PostGIS 12 及以上版本。这一经历再次印证了遵循协调漏洞披露政策的重要性,项目方呼吁所有用户在新版本发布时及时更新。 此外,2026 年 6 月 11 日随 GeoServer 3.0.0 版本发布,还公开了以下 CVE:GeoServer 2.27.3 和 2.26.4 版本涉及 CVE-2025-58175(XML 实体解析中的服务器端请求伪造 SSRF,中危)和 CVE-2025-52465(主密码转储页面中的任意文件写入,高危);GeoServer 2.27.0 版本涉及 CVE-2024-45747(处理 FreeMarker 模板时的服务器端模板注入 SSTI,高危)和 CVE-2025-27511(DB2 存储连接中的 JNDI 漏洞,高危)。 供应链安全公告同样值得关注,因为它们可能影响下载软件的完整性。2026 年 4 月,安全研究员 Aviv Donenfeld 报告了 geoserver-cloud 仓库 GitHub Actions 工作流中的一个问题(GHSA-cpc9-c4h3-2jwx)。
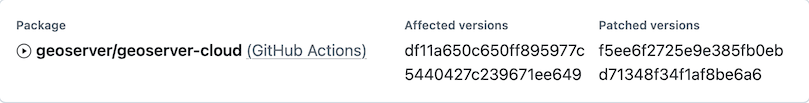
虽然 GeoServer 使用 GitHub 进行源代码管理和质量保证工作流,但这些工作流并不用于构建或发布下载制品。项目方已进行审查,确认漏洞期间的所有拉取请求均来自可信方,密钥已轮换,工作流问题也已解决。这是项目首次处理此类基础设施安全公告。需要强调的是,没有任何 GeoServer 正式版本受到影响,因为 GeoServer 版本是通过 Jenkins 构建服务器发布制品至 SourceForge 和 OSGeo 基础设施的。 与许多其他软件项目一样,GeoServer 正面临大量由 AI 辅助生成的漏洞报告。项目方已制定通用 AI 政策并更新了安全政策,以认可这些工具的使用并提供指导。AI 报告通常非常冗长,报告者若能随时澄清将大有帮助。审查这些报告、甚至判断是否为重复报告都可能耗费大量时间。如果报告者能够测试并验证修复程序,也将对项目大有裨益。项目方呼吁,如果您的组织依赖 GeoServer,请考虑赞助该项目,或让您的员工直接参与 geoserver-security 工作。同时,项目方也在寻求为面临赞助和参与限制的公共机构建立项目成员资格。 GeoServer 采用限时发布周期,每年维护“稳定版”和“维护版”。请至少每年升级一次至受支持的版本,以持续获得安全修复。有关如何私下报告漏洞的说明,请参阅项目的安全政策。想了解完整技术细节和原始公告,请点击阅读原文。
编译自 Planet OSGeo,原文链接
原文摘要
GeoServer Security Update - September 2026
This post provides a recap of the security advisories published over the summer of 2026, covering recently published Common Vulnerability and Exploits (CVE), along with a supply chain advisory affecting the GeoServer project. This activity has resulted in an update to our security policy covering AI-assisted vulnerability reports. If you are responsible for a GeoServer instance, the short version is: please update to , , or .GeoServer 3.0.1GeoServer 2.28.5GeoServer 2.27.6 The GeoServer project follows a coordinated vulnerability disclosure policy: vulnerabilities are fixed for both stable and maintenance releases, prior to CVE details being published. The goal is to give everyone an opportunity to update prior to public disclosure. In August GeoServer experienced a zero-day vulnerability (an exploit in the wild with no known fix). The problem had already been reported privately by several independent researchers, and a fix scheduled for the GeoServer 3.0.1 release. The zero-day situation arose because a third party (unconnected to the project or to the researchers who had reported the issue) disclosed the vulnerability publicly on social media. The effect was immediately evident, with scans for this vulnerability detected within hours of the public social media post. The speed of this response was remarkable and resulted in and an urgent call to update on our . We would like to thank the reporter Ravie Lakshmanan who first notified project leadership via the Open Source Geospatial Foundation.news coverageuser forum GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6: This experience reaffirms the importance of following the coordinated vulnerability disclosure policy, and asking everyone to update when new releases are made available. The following CVEs were published on June 11, 2026, alongside the .GeoServer 3.0.0 release GeoServer 2.27.3, and 2.26.4: GeoServer 2.27.0: Supply chain advisories have the possibility to affect the integrity of the software you d